
Shadow IT is any software, app, device, or cloud service that employees use for work without the knowledge or approval of the IT department. It usually starts with good intentions, like getting work done faster, but it creates security, compliance, and cost risks the business can’t see.
Think of the team that shares files through a personal Dropbox account, the manager who signs up for a project management tool on a company credit card, or the employee who pastes customer data into a free AI chatbot. None of these people are trying to cause harm. But each one creates a gap that IT can’t protect, because IT doesn’t know it exists.
Below, we explain why shadow IT happens, common examples, the real risks, how shadow AI fits in, and how to detect and manage it without slowing your team down.
Why Does Shadow IT Happen?
Shadow IT happens when employees feel the approved tools don’t meet their needs, or the approval process takes too long. The most common reasons are:
- Speed: Signing up for a free app takes minutes. Waiting for IT approval can take weeks.
- Better tools: Employees may find a consumer app easier to use than the company’s official system.
- Remote and hybrid work: People working from home are more likely to use personal devices and apps.
- Easy cloud sign-ups: Most SaaS tools only need an email address and a credit card.
- Lack of awareness: Many employees simply don’t know there’s a policy, or don’t see the risk.
Shadow IT Examples
Shadow IT can be almost anything that touches company data. Common examples include:
- File sharing: Personal Google Drive, Dropbox, or WeTransfer accounts used to share work documents.
- Messaging apps: WhatsApp, Telegram, or personal Slack workspaces used for client or team conversations.
- Productivity and project tools: Trello, Notion, Asana, or similar tools set up by a team without IT involvement.
- Personal devices: Laptops, phones, or USB drives that aren’t managed or secured by the company.
- Browser extensions and plugins: Add-ons that can read everything on the pages employees visit.
- Unapproved cloud services: Servers, databases, or hosting accounts spun up by a developer or department outside of IT.
- Spreadsheets and macros: Critical business processes running on one person’s unshared spreadsheet.
- AI tools: Free chatbots, writing assistants, or AI note-takers used with company or customer data.
What Are the Risks of Shadow IT?
The biggest risk of shadow IT is that you can’t protect what you can’t see. Specific risks include:
- Data leaks: Sensitive files stored in personal accounts can be shared, lost, or exposed without anyone noticing.
- Security gaps: Unapproved apps may lack strong passwords, multi-factor authentication, or security updates, giving attackers an easy way in.
- Compliance problems: Privacy laws require businesses to know where personal data is stored. In Canada, that includes PIPEDA and, for businesses operating in Quebec, Law 25. Data sitting in unknown apps makes this impossible to prove.
- Lost data when people leave: If an employee’s personal account holds company files, those files can leave with them.
- Integration and data quality issues: Information gets split across disconnected tools, so no one has the full picture.
Our posts on common cybersecurity mistakes and the guide to cyber security in Canada cover these threats in more detail.
What Are the Hidden Costs of Shadow IT?
Shadow IT often looks free, but it carries costs that don’t show up until later:
- Duplicate subscriptions: Different teams pay for the same or similar tools without knowing it.
- Wasted licences: Paid accounts stay active long after the person who set them up has moved on.
- Breach and recovery costs: A single exposed account can lead to investigation, recovery, and legal costs far higher than any subscription.
- Support time: IT gets pulled in to fix tools it never set up and doesn’t fully understand.
- Technical debt: Disconnected tools and workarounds pile up over time, making future changes slower and more expensive. Learn more in our guide to technical debt.
What Is Shadow AI?
Shadow AI is the use of AI tools, such as chatbots, writing assistants, code generators, and AI note-takers, without IT approval or oversight. It’s the fastest-growing form of shadow IT, because AI tools are free or cheap, easy to access, and genuinely useful.
The main risk is what employees put into these tools. Pasting customer details, contracts, financial data, or source code into a public AI service may mean that data is stored, logged, or used in ways the business didn’t agree to. AI-generated content and code can also be inaccurate or insecure if no one checks it.
Shadow IT vs Shadow AI
| Shadow IT | Shadow AI | |
|---|---|---|
| What it is | Any unapproved app, device, or service | Unapproved AI tools and features |
| Typical examples | Personal cloud storage, messaging apps, unmanaged devices | Free chatbots, AI writing tools, AI meeting note-takers, code assistants |
| Main risk | Data stored where IT can’t secure it | Sensitive data shared with outside AI models, plus unchecked AI output |
| How it’s spotted | Network monitoring, SaaS discovery, expense reviews | The same methods, plus browser and AI usage monitoring |
| Best response | Offer approved alternatives and a clear policy | Offer approved AI tools and a clear AI use policy |
How to Detect Shadow IT
You can detect shadow IT by looking for apps and services in the places they leave traces:
- Review expenses and card statements: Look for recurring software charges on company or reimbursed cards.
- Check single sign-on and identity logs: See which outside apps employees connect with their work accounts.
- Monitor network and DNS traffic: Identify connections to cloud services that aren’t on your approved list.
- Use SaaS discovery or CASB tools: Cloud access security brokers and SaaS management tools can map which apps are in use.
- Audit browser extensions and devices: Endpoint management tools show what’s installed on company devices.
- Ask your team: A simple, no-blame survey often uncovers more than any tool.
How to Manage Shadow IT
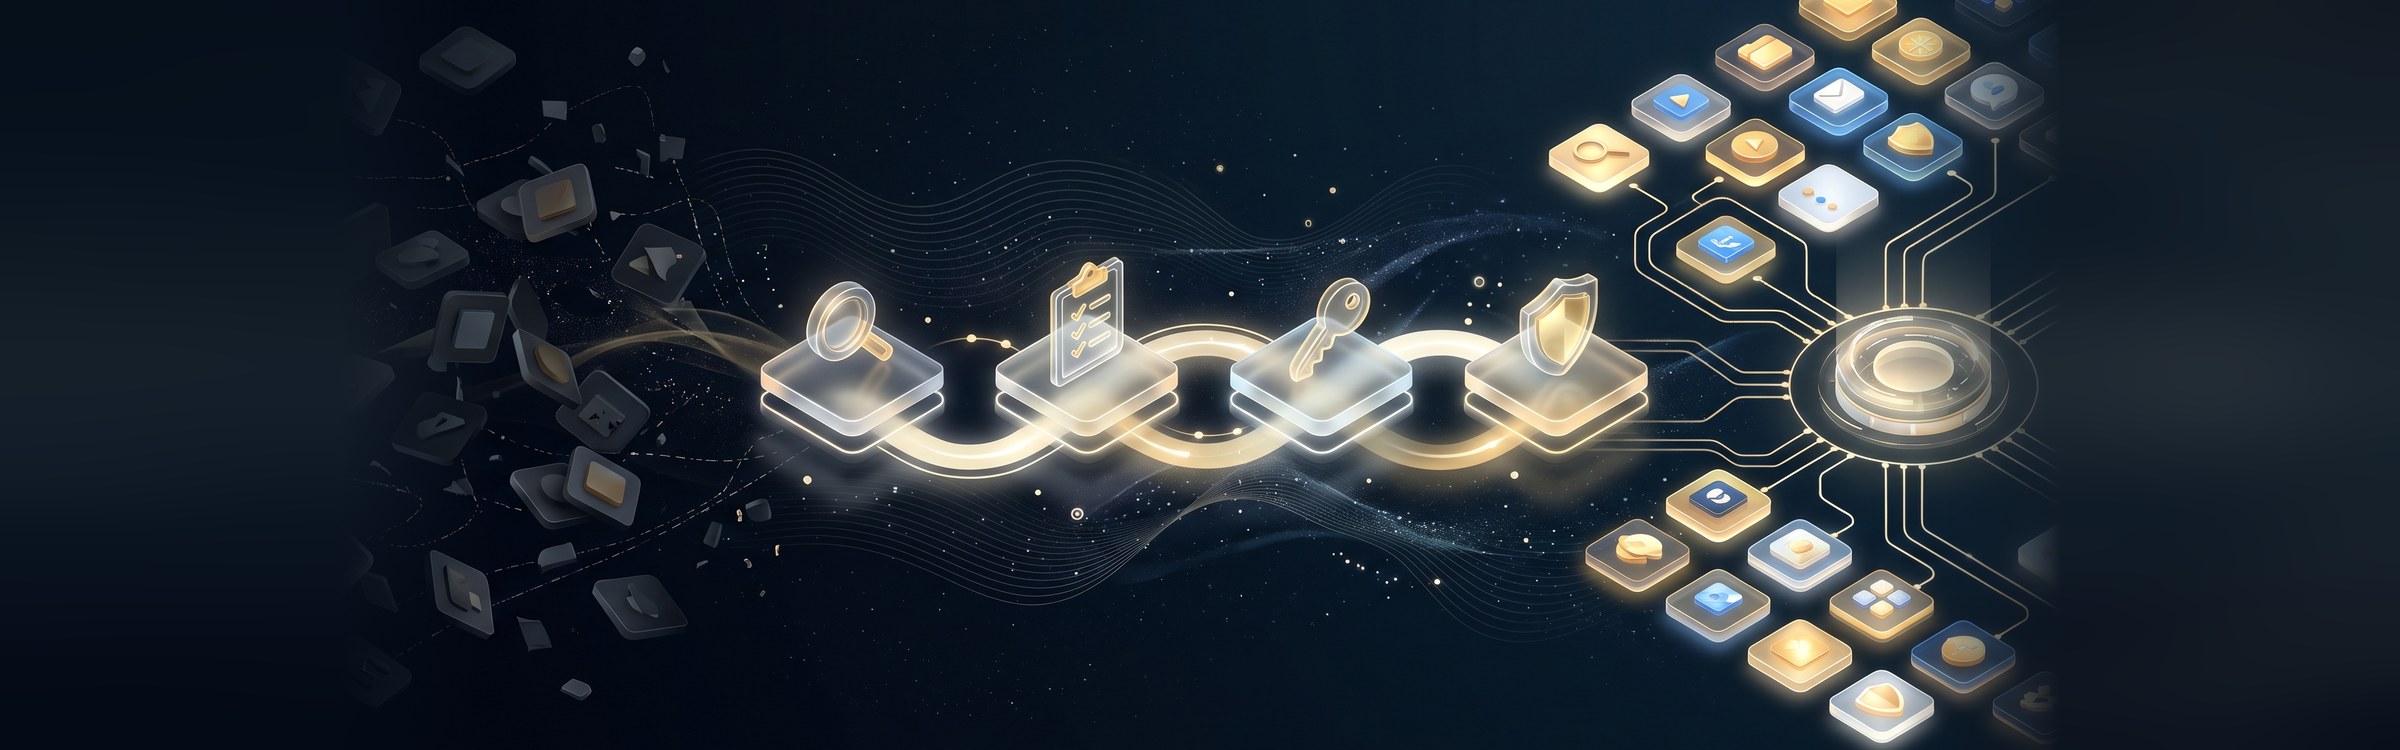
Trying to ban every unapproved tool rarely works. People find workarounds. A better approach is to bring shadow IT into the light:
- Find out what’s in use: Build an inventory of apps and services using the detection methods above.
- Understand why: Ask teams what problem each tool solves. Often it points to a gap in your approved tools.
- Approve, replace, or remove: Bring useful tools under IT management, offer a secure alternative, or retire risky ones.
- Create a clear, simple policy: Explain what’s allowed, what isn’t, and how to request a new tool. Include a section on AI use.
- Make approval fast: A quick request process removes the main reason people go around IT.
- Secure the basics: Use single sign-on, multi-factor authentication, and device management so approved tools are both easy and safe.
- Connect your systems: When approved tools work together, people have less reason to build their own workarounds. Our guide to API integration explains how.
- Train and repeat: Short, regular reminders work better than a one-time policy email.
For many small and mid-sized businesses, a managed IT partner handles much of this, from monitoring and device management to policy and user support. Our post on managed IT services explained covers how that works.
Is Shadow IT Ever a Good Thing?
Shadow IT can be a useful signal. When employees go looking for their own tools, it often means they need something the business hasn’t provided. Treated the right way, shadow IT can point you toward better software, faster processes, and smarter use of the cloud. The goal isn’t to stop people from finding better ways to work. It’s to make sure those tools are visible, secure, and supported.
Frequently Asked Questions
What is shadow IT in simple terms?
What is an example of shadow IT?
Why is shadow IT a security risk?
What is the difference between shadow IT and shadow AI?
How do you stop shadow IT?
Bring Shadow IT Into the Light
Shadow IT isn’t a sign that your team is careless. It’s a sign they want to get work done. The answer is visibility: know what’s being used, give people secure tools that actually meet their needs, and set clear, simple rules, including for AI.
At BitWaves, we help businesses across Canada and the US discover, secure, and manage the tools their teams rely on. Explore our managed IT services, or get in touch to talk about getting shadow IT under control.